We think like the attacker.
To better defend
your business.
Offensive intelligence, 24×7 defensive operations and risk governance, powered by proprietary AI and validated by senior specialists.
Specialists and AI.
On the same team.
Senior specialists deliver the services. Three proprietary platforms add scale and show, every day, where your exposure stands.
- Offensive Security
- Defensive Security
- Governance, Risk and Compliance
- Fraud Hunting
Four fronts.
One partner.
From simulated attack to governance, end to end. The people defending your environment have been on the other side.
Offensive Security
We attack your defenses with the sophistication of a real adversary, so the gap is found by us, not by a criminal.
2 services
Pentest
Applications, APIs, networks and cloud. We chain vulnerabilities, prove the impact and deliver a prioritized remediation plan.
Counterintelligence
We track advanced threats: deep and dark web, phishing kits, leaked credentials, attribution and containment.
Defensive Security
Real-time detection and response. When the threat shows up, we're already there.
4 services
24×7 SOC
Continuous monitoring, AI triage and investigation by senior analysts. From hours to minutes.
Incident Response
Containment, eradication, root cause and recovery. During an active crisis or on retainer.
First Response
On call for the first hour: isolation, containment and evidence preservation.
Digital Forensics
Chain of custody, timeline and an expert report with evidentiary value.
Governance, Risk and Compliance
Security isn't just technology. It's strategy, compliance and people.
4 services
Advisory and vCISO
Security program, prioritized roadmap and CISO as a service to take risk to the board.
Cyber Compliance
LGPD, ISO 27001, PCI-DSS, AML and Central Bank of Brazil (BACEN) rules translated into practical, audit-ready controls.
Human Factor
Training tracks and simulated phishing campaigns, with micro-training at the point of failure.
AI Governance
Governance framework, data policies and model monitoring. NIST AI RMF and ISO/IEC 42001.
Fraud Hunting
We start from the premise that fraud is already happening and hasn't been seen yet. Proactive search, without waiting for the alert.
4 services
Continuous Hunting
Fraud hypotheses formulated and hunted across transactions, access and customer journeys. Predictive investigation, not alert reaction.
Insider Fraud and Collusion
Privilege abuse, orphaned accounts, irregular approvals and collusion among employees, partners and third parties.
Payment Fraud
Pix, cards, onboarding and account takeover: we rebuild the fraudster's path and close the gap.
Anti-Fraud Intelligence
Deep and dark web, fake brands, leaked data and malicious profiles correlated with your data.
Findings this session
CVEs cataloged in VExDay
under active exploitation
evidence items collected by the AI
continuous detection and response
VExDay and Truehacking.ia data, September 2026.
Three platforms.
One for each question the board asks.
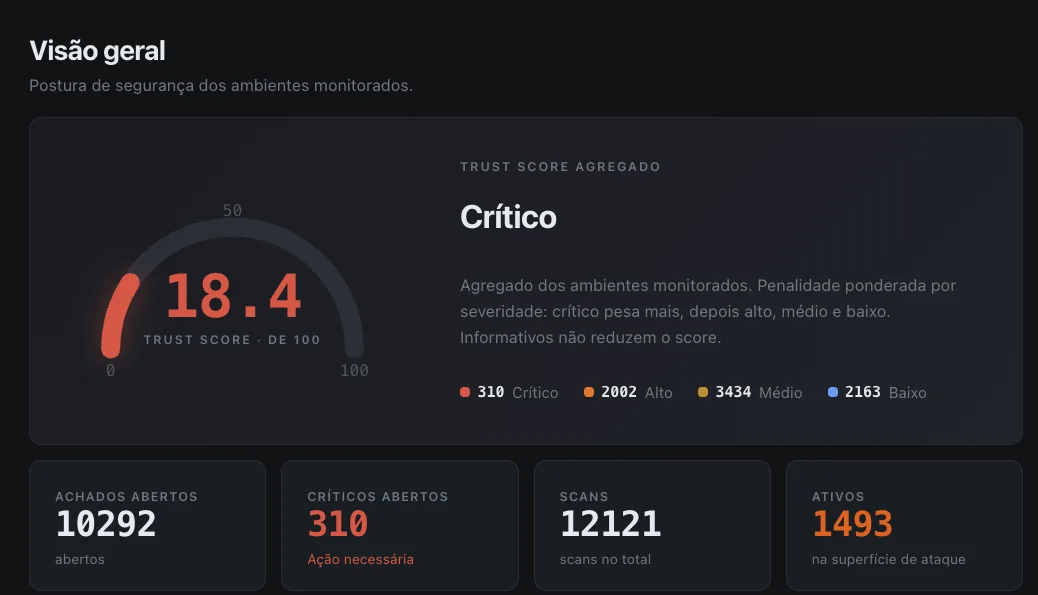
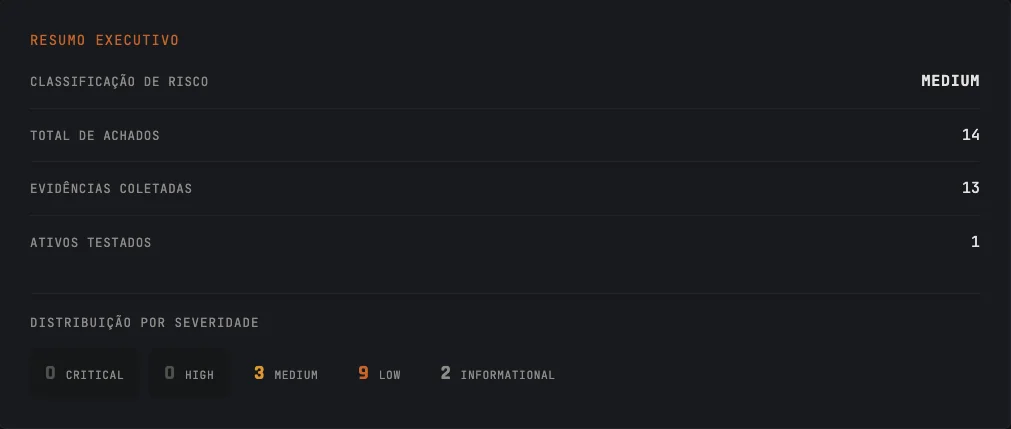
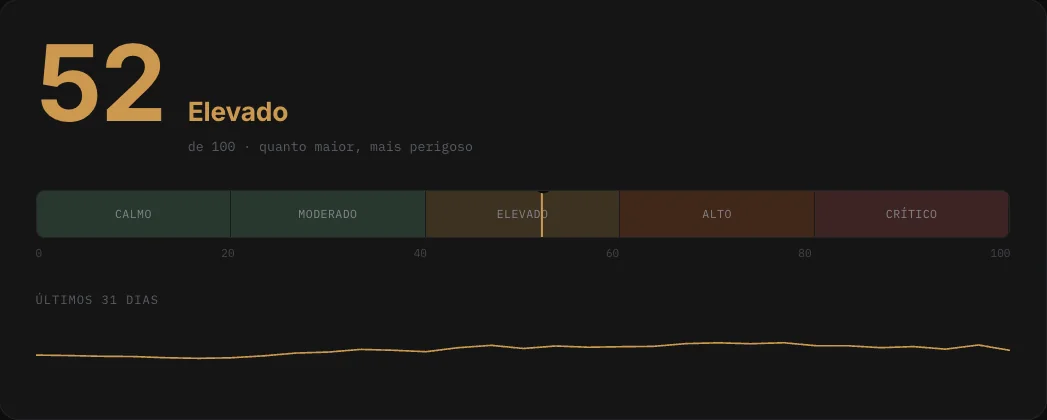
From autonomous pentesting to real-time threat intelligence, amplifying every engagement.
Findings by severity
Aggregate trust score
Brazil risk · daily index
Being exploited now
For those who take security seriously.
From startups to banks.
We serve companies of every size and industry, with extra depth where risk is regulated and money is at stake. We know the requirements of the Central Bank of Brazil, PCI-DSS and LGPD, and the attack vectors aimed at financial institutions.
Anti-fraud and KYC
Onboarding, biometrics, liveness and device.
Account takeover prevention
Continuous authentication, session and password recovery.
AML and transactions
Pix and card monitoring, AML and BACEN compliance.
Fraud Hunting
Proactive hunting for hidden fraud in transactions and access.
Everyday regulation: BACEN, PCI-DSS, LGPD and AML.
Talk to our new business teamMost organizations discover their vulnerabilities at the worst possible moment: during the attack.
Our clients get ahead of them with our services and platforms.
We think like the attacker
Our offensive background improves the defense with our own threat intelligence.
End-to-end operation
From pentesting to governance, a single partner covers the entire risk cycle.
Proprietary AI
Truehacking.ia, TrustSentinel and VExDay amplify every engagement.
Senior team
Senior professionals with over 20 years of experience.
Maturity focus
We help companies scale their cybersecurity maturity.
Fraud hunting
Proactive fraud hunting across digital and financial ecosystems.
Protecting those who can't stop.
From simulated attack to regulatory compliance, with one goal: bring cyber risk down to a level where the business can grow with confidence.
Machines to scale
Proprietary AI expands coverage and speed: it maps the surface, generates attack vectors at scale and triages millions of events.
Humans to decide
Senior specialists corroborate results, eliminate false positives and translate technical risk into business decisions.
What backs
every engagement
- People
- Senior team with over 20 years of experience across offense, defense, governance and fraud
- Method
- MITRE ATT&CK, OSSTMM, OWASP, NIST SP 800-115, PTES and TIBER-EU
- Compliance
- ISO/IEC 27001, PCI-DSS, LGPD, BACEN and ISO/IEC 42001
VExDay daily briefing
What changed in the last 24 hours, in decision-maker language.
CVEs under active exploitation, ransomware groups targeting Brazil and the day's risk index, in a summary that fits before your first meeting.
Frequently asked questions. Straight answers.
Didn't find what you were looking for? Talk to us
What does TrueHacking do?
We protect companies across four fronts: offensive security, defensive security, governance, risk and compliance, and fraud hunting. The work is done by a senior team and backed by three proprietary AI platforms: Truehacking.ia, TrustSentinel and VExDay.
Do you only work with banks and fintechs?
No. We serve companies of every size and industry. We have extra depth in regulated sectors such as finance, but the method is the same for any company that takes security seriously.
Do I need to hire services and platforms together?
No. You can hire only our specialists, use only the platforms, or combine both. Many clients start with a service, such as a pentest, and later adopt a platform for continuous visibility.
What's the difference between Truehacking.ia and a traditional pentest?
Truehacking.ia uses AI to map the surface, generate attack vectors at scale and collect evidence, at the continuous pace the business demands. Senior specialists validate every finding and remove false positives. The result comes in two reports: an executive one and a technical one.
How does a pentest with you work?
We define the scope with your team, execute following MITRE ATT&CK, OSSTMM, OWASP, NIST SP 800-115 and PTES, and chain vulnerabilities to prove the real impact. At the end, you get a prioritized remediation plan.
Do you help with LGPD, ISO 27001 and PCI-DSS?
Yes. Our governance, risk and compliance front includes consulting, vCISO and alignment with standards such as ISO/IEC 27001, PCI-DSS, LGPD, Central Bank of Brazil requirements and ISO/IEC 42001 for AI governance.
I'm under attack right now. What should I do?
Contact us immediately through the incident channel. Our First Response team acts in the first hour: isolation, containment and evidence preservation. See how to reach us
How much does it cost?
It depends on the scope, the size of the environment and the frequency. After an initial conversation, we send a tailored proposal. Book a conversation
How secure is
your organization?
Find out in a 30-minute conversation with a senior specialist, no commitment.
Under attack right now?
Our First Response team acts in the first hour: isolation, containment and evidence preservation.
Write to contato@truehacking.com.br with INCIDENTE (incident) in the subject line.